Get your clients audit-ready before the real auditor walks in.
AuditVanguard collects security evidence from Okta, AWS, and GitHub, maps it to SOC 2, ISO 27001, HIPAA, and more, and packages it for the auditor. No last-minute scrambling.
No SOC 2 report means lost enterprise deals. A failed audit means months of delay.
For consultants and compliance firms preparing clients for SOC 2, ISO 27001, HIPAA, PCI DSS, CMMC 2.0, and GDPR.
We don't scan code and we don't issue the audit. We get you ready for it.
$199/month, unlimited clients. Free demo client, no card.AI maps your evidence to controls and produces branded audit reports.
One workspace per client, with evidence collection, an auditor portal, and a tamper-evident audit trail, for one flat $199/month and unlimited clients.
Consultants and compliance firms getting clients ready for their next compliance audit.
Okta · AWS · GitHub · PDF export.
How it works
Connect Okta, AWS, and GitHub, or upload files.
See AuditVanguard in Action.
A short walkthrough of how it works — from evidence to audit-ready report.
Demo narration transcript
- Intro. I'm Godwin, founder of AuditVanguard. Still running audits on spreadsheets and email? AuditVanguard puts your whole audit in one secure workspace.
- Connect your frameworks. Pick your frameworks, and the control baseline applies instantly.
- Map your controls. AI cross-maps every control and flags the gaps. Drop in evidence, and Magic Mapping matches it for you.
- Export audit-ready reports. Then export a branded, audit-ready report backed by a tamper-evident audit trail.
- Closing. From framework to sign-off — create your secure workspace at AuditVanguard.com.
Every tool your practice needs.
Purpose-built for GRC.
AuditVanguard replaces the shared Google Drive, the tangled email thread and the last-minute report scramble with one workspace designed for compliance work.
Here is exactly what we collect and organize for you:
Access logswho logged in, when, and from where
Security policiespassword, clean desk, acceptable use, and more
System configurationsproof your controls are actually turned on
Training recordsevidence your team completed required security training
Vendor agreementscontracts and security assessments for third parties
Incident recordsdocumented responses to any security events
Evidence arrives by upload or through live read-only connectors for Okta, AWS and GitHub.
Multi-tenant Portal
Every client gets an isolated workspace with their own login. Notes, files, tasks and evidence never cross tenant lines.
Zero-Touch Onboarding
Share your intake link — prospects enter their company, contact and frameworks, and a ready-to-work workspace appears in your dashboard with your baselines applied.
Compliance Templates
Save your firm's baseline notes per control once. Every new client starts with a strong draft — not a blank page.
Branded PDF Exports
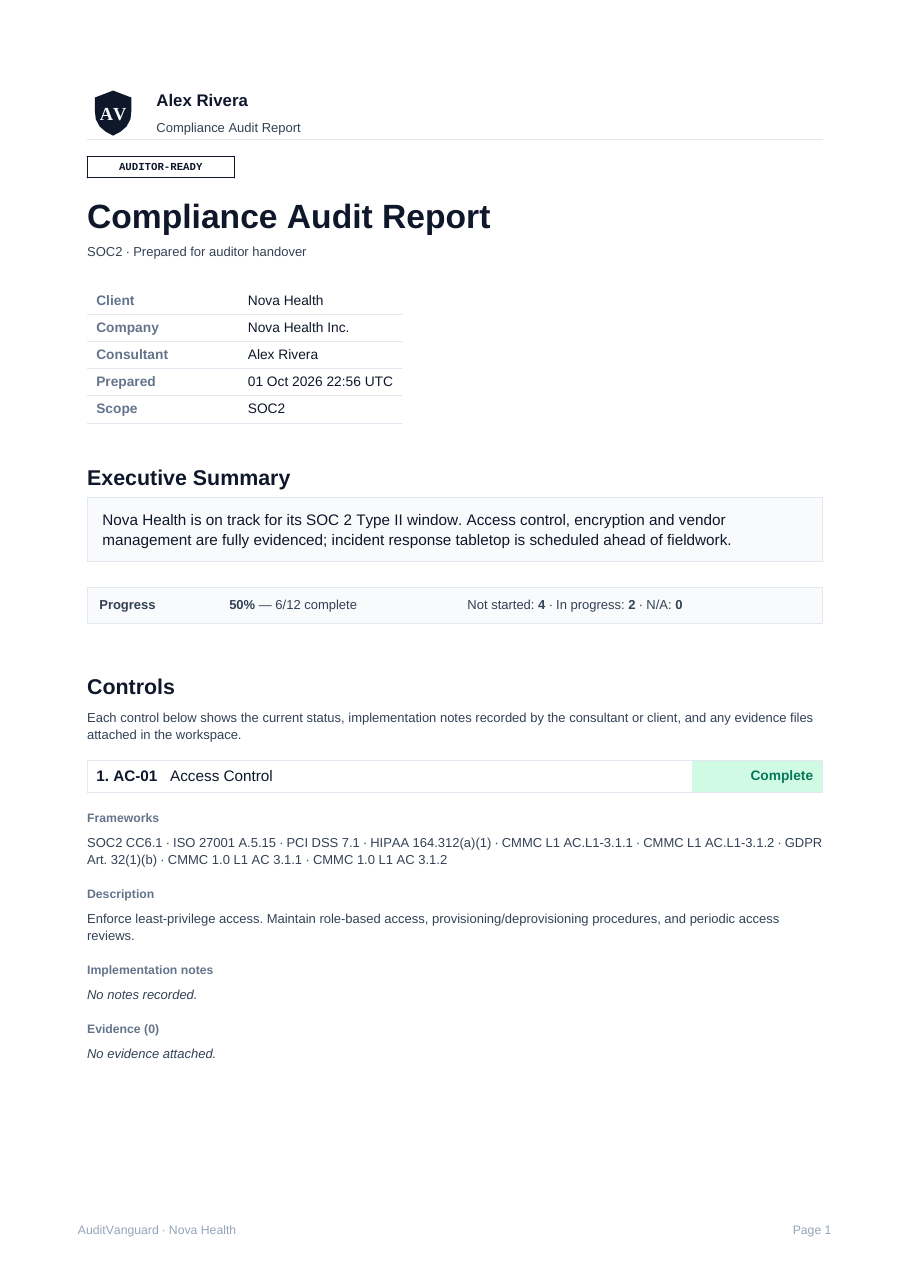
One-click audit reports with your logo, firm name and executive opinion on the cover. Every generated PDF is versioned and archived per client, so you can re-share the exact snapshot without regenerating.
Client communication and reminders
Direct messaging keeps the audit conversation organized — no more chasing evidence through email. Automatic nudges fire when a control sits in-progress for 30 days with no evidence, so nothing slips.
Policy Template Library
Curated policy templates for SOC 2 and ISO 27001 — Clean Desk, BYOD, Incident Response — that you share with a click to jumpstart client compliance.
Built for the
AI compliance era.
Automated audit trails, cross-framework coverage, AI-native evidence review, and a real Auditor Portal — the pillars compliance firms and their auditors have been asking for.
Live read-only connectors for Okta, AWS and GitHub. How it works: 1 — connect with least-privilege read-only credentials, 2 — AuditVanguard ingests MFA coverage, stale credentials, branch-protection gaps, dependency alerts and log coverage, 3 — each finding lands on the right control automatically.
Integration docs & required permissions →Full cross-mapping for SOC 2, ISO 27001, ISO 42001 (AIMS), PCI DSS, HIPAA, CMMC 2.0 (Level 1 & 2), GDPR, NIST AI RMF and the new EU AI Act (Articles 9, 10, 13, 14, 15, 62). One control, every framework.
Every action — file uploads, note edits, task status, control state changes, PDF exports, auditor comments — is written to a SHA-256 hash-chained log that timestamps itself. Non-editable, tamper-evident, and exportable as a signed JSON any third party can verify.
Verify a signed log →| Feature | Status |
|---|---|
| Okta connector (read-only) | Live |
| AWS connector (read-only) | Live |
| GitHub connector (read-only) | Live |
| Auditor Portal | Live |
| Branded PDF exports | Live |
| EU AI Act control mapping | Live |
| Microsoft Entra ID connector | Roadmap |
| Google Workspace connector | Roadmap |
| Jira connector | Roadmap |
| Nightly connector auto-sync | Live |
Pricing.
One firm-wide price: $199/month, unlimited clients.
Every workflow,
answered by AI.
AuditVanguard's assistant lives inside every control, every file, and every auditor flag — grounded in your client's own evidence, not the open internet. Client data is not used to train models.
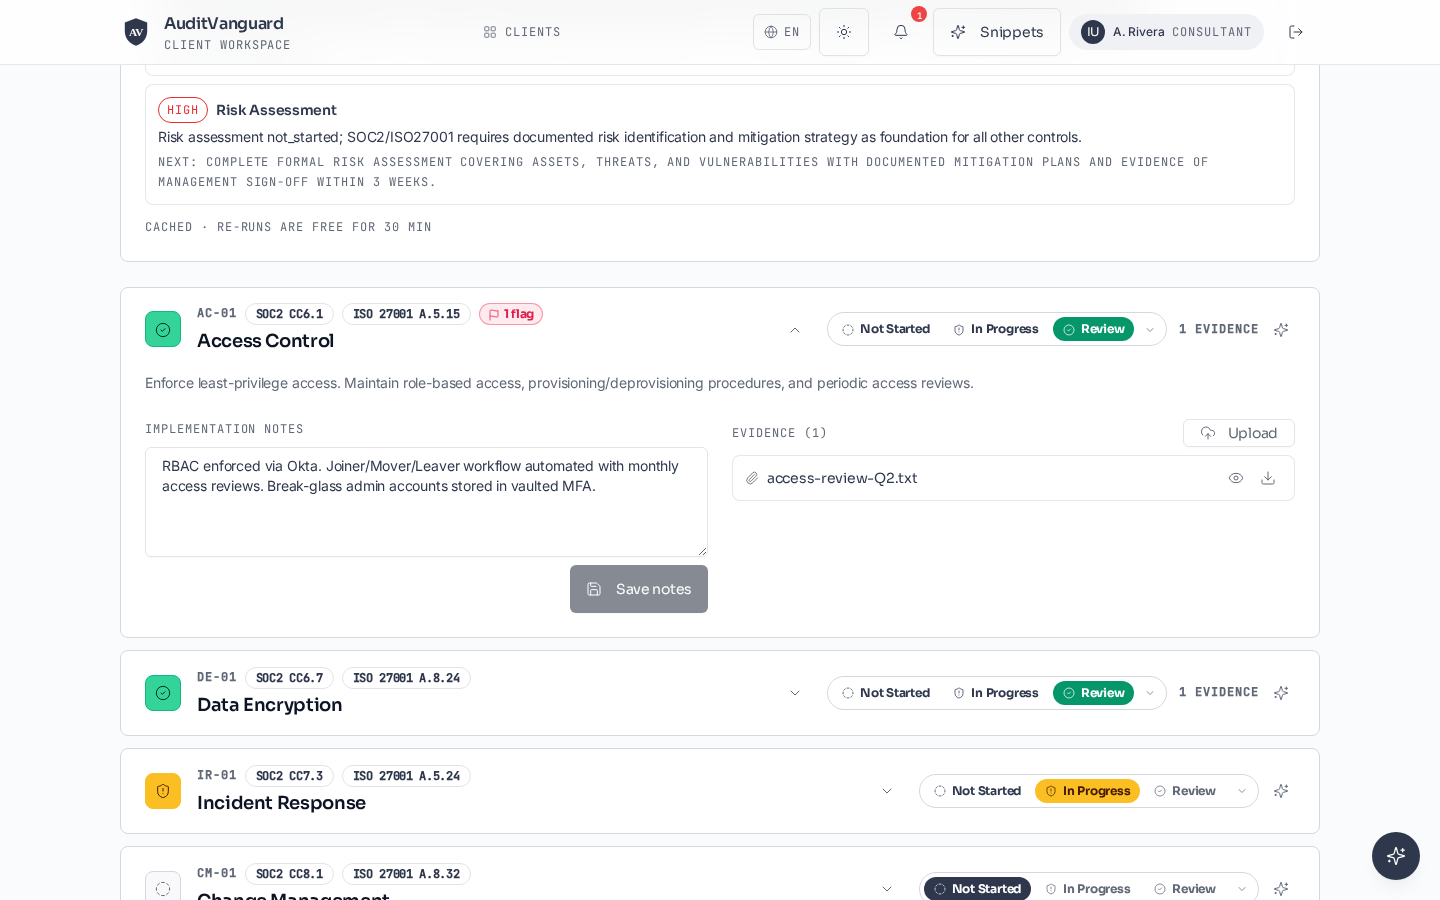
Drop an evidence file — AuditVanguard reads it and suggests the exact controls it satisfies across every framework. No more tagging matrices by hand.
Ask a plain-English question about any control or auditor flag and get an expert-grade answer, cited to the client's own evidence and notes. Right where you're working.
AI runs a live gap analysis on every workspace — the top three risks, the fastest wins, and the exact controls holding back an audit sign‑off.
The whole compliance audit lifecycle.
Under one roof.
From client onboarding to auditor sign‑off — consultants, clients and official auditors work in the same workspace with the same source of truth. No email chains. No lost evidence.
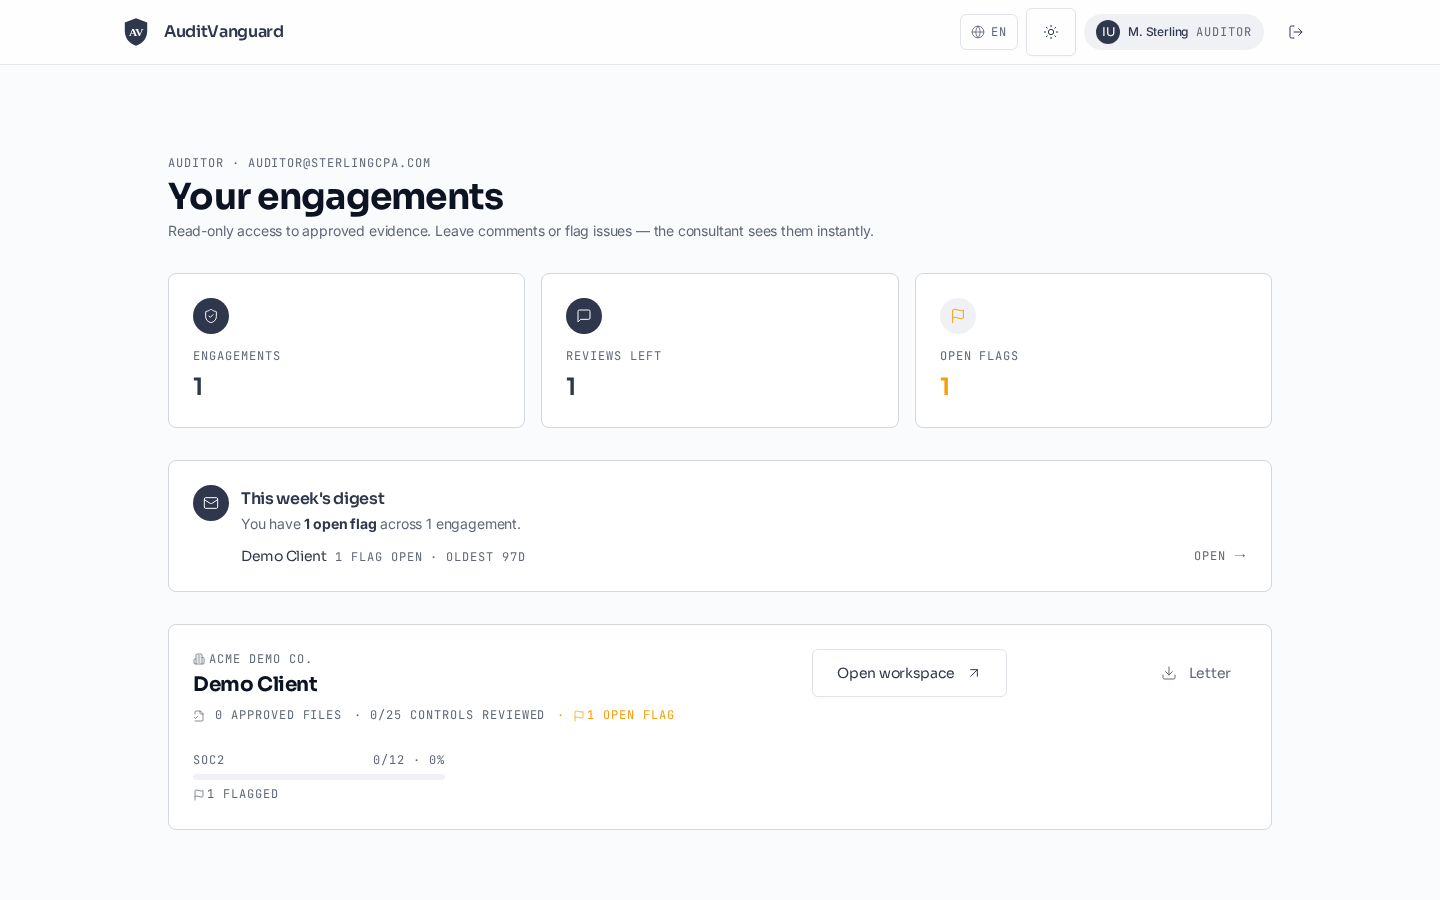
Auditors flag any control or file with a priority. You and the client reply in-thread with screenshots and links. Bulk-resolve when the queue is done.
NDA-gated access with versioned evidence history. Every download is logged.
Invite official auditors into a dedicated read-only workspace. They review the same evidence you and the client see — without email attachments or file exports.
Pilot customer results. Shared with permission.
AuditVanguard is designed, built and operated by Godwin Oiku, a cybersecurity practitioner with 12+ years across IT and security.
PMP · CompTIA Security+ · CySA+ certified.
Inside the product
Real screens from the live product — swipe through on mobile.
Isolation is not
a feature. It's the default.
Every client tenant is enforced at the API layer with request-scoped role checks. Passwords are bcrypt-hashed, JWTs are short-lived, and every evidence upload lives in a per-tenant object-storage path.
All /clients/{id}/* endpoints check ownership on every request.
Passwords hashed with a per-user salt; tokens signed with a rotating secret.
Every PDF export is version-locked in object storage.
No user enumeration on password reset. 60-min single-use tokens.
Building toward the compliance we help you deliver.
Aligned to SOC 2 Trust Services Criteria. Independent audit not yet started.
- Tenant isolation enforced at the API layer on every request
- SHA-256 hash-chained, tamper-evident audit log
- Independent penetration test: planned
See it on your own engagements.
Leave your work email and we'll schedule a 30-minute walkthrough — no commitment, no card.